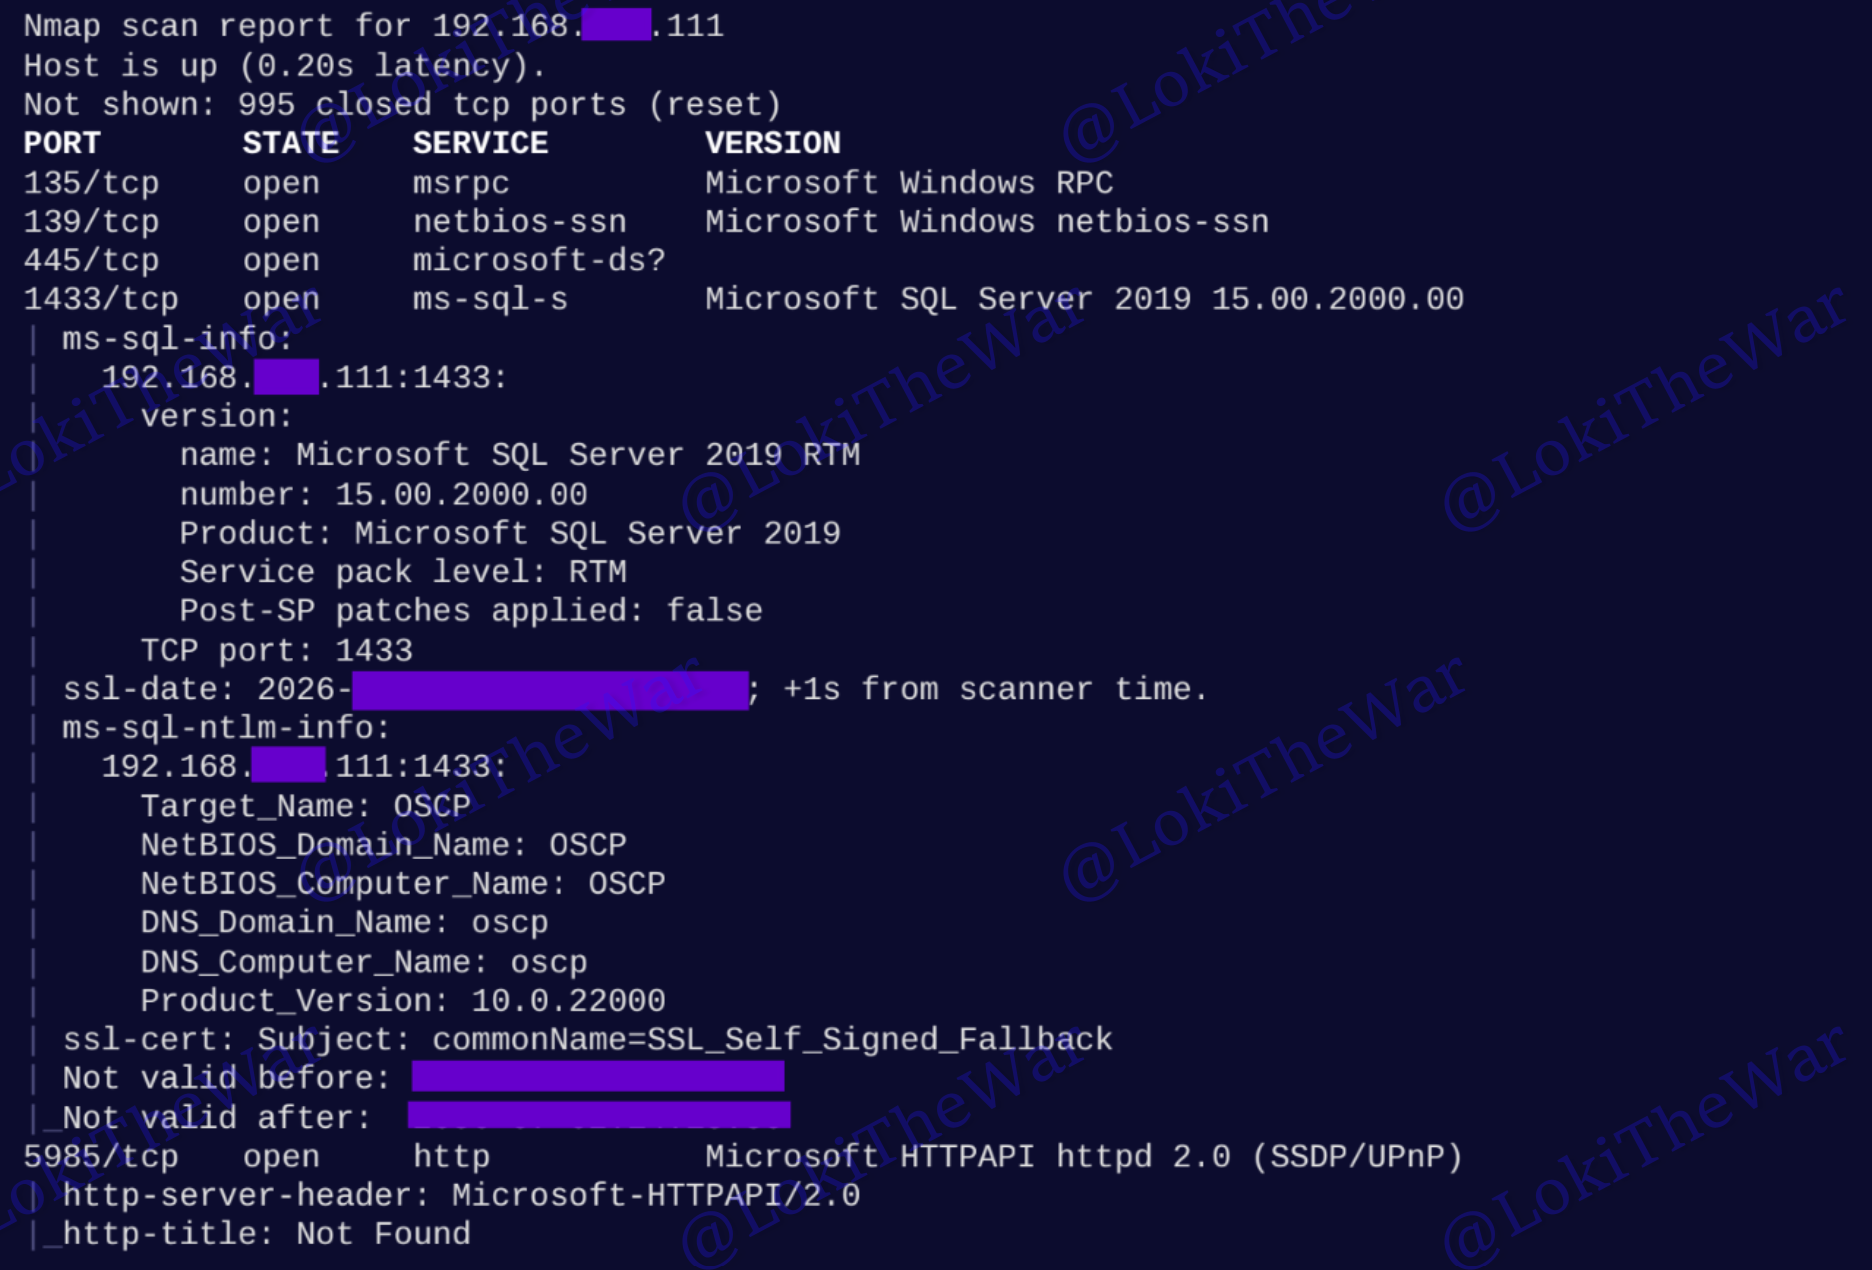
OSCP+ .111 135 139 445 1433 Standalone Machine Report
Paid: $0.00
Payment Confirmed! 🎉
Your download link has been sent to your email address. Please check your inbox (and spam folder).
OSCP+ .111 ''MS SQL Server'' Standalone Machine (10 Points)
- 1433 (Microsoft SQL Server 2019 15.00.2000.00 RTM)
- 135, 139, 445 (Microsoft Windows RPC & SMB)
- 5985 (Microsoft HTTPAPI httpd 2.0 - WinRM)
Payment accepted: PayPal, credit cards, debit cards, and cryptocurrency.
Need help choosing? Reach out to OSCPPREP directly:
OSCP+ .111 "MS SQL Server" Standalone Exploitation Methodology
Standalone targets on the PEN-200 exam are typically split into 10 points for initial access and 10 points for privilege escalation. Securing the first 10 points on this OffSec OSCP+ standalone machine requires targeted enumeration of database services. The .111 Windows target prominently features Microsoft SQL Server 2019 (version 15.00.2000.00) running on port 1433[cite: 7], alongside standard Windows administration protocols like SMB (445) and WinRM (5985)[cite: 7]. This guide breaks down the exact methodology needed to interface with the SQL Server, execute database-level attacks, and secure a stable reverse shell for your initial 10 points.
Instead of burning hours of your exam window falling down enumeration rabbit holes or testing dead-end exploits against hardened SMB services, this report gives you the direct, verified exploitation sequence for the MS SQL vector. We provide the exact terminal syntax required to exploit the running services, ensuring you can copy, paste, and execute your way to the user flag rapidly.
Target Profile & Exam Readiness
• Active OSCP Candidates: Guarantee your 10 points early in the exam. This guide ensures you don't fail by missing the initial foothold on this database-heavy machine.
• Tactical Execution: Avoid syntax errors under pressure. Rely on pre-formatted commands designed for instant terminal execution and reliable output.
• Complete Documentation: Includes the necessary command flows to ensure your final exam report is properly documented for this specific target.